Regulated financial operations, run with forensic precision.
KYC/AML, synthetic-ID fraud monitoring, disputes, payments operations and loan processing — delivered by secure, PCI-DSS 4.0–compliant Manila teams that measure performance in Risk-Adjusted Yield, not headcount.
Regulated finance is one of the most demanding corners of the market, and this page sits inside our broader guide to outsourcing to the Philippines, which covers how the whole delivery model works before any single industry gets its own rules.
Our KYC vendor has the lowest cost per FTE — what does that invoice hide?
The miss rate. A 150-FTE operation passing 10,000 identities at 26% synthetic-ID miss rate bills identically to one at 3%; the ~$520K a month in fraud loss never reaches the invoice. Measured per clean verification (RAYVI), lender FS-037 fell from $35.40 to $6.70 after moving to 40 specialists plus AI: miss rate 2.7%, case cycle 3.1 days to 5.2 hours.
BPO Suppliers
Institutions Served
Philippines
Philippine financial-services outsourcing has crossed a structural threshold. The conversation has moved from cost-per-FTE to Risk-Adjusted Yield per Verified Identity — a metric that rewards Agentic-AI accuracy, Zero-Trust security and Manila’s irreplaceable SEC/FINRA/FCA fluency over raw headcount volume.
A complete financial-operations stack, outsourced.
Where your risk concentrates decides what you outsource first.
Onboarding volume is where the Tripartite Composite hides. Agentic + HITL identity proofing, sanctions/PEP screening, and dispute operations built for high-velocity retail books.
Where the work is a live conversation with a cardholder, borrower or account holder rather than a case in a queue, the rules for staffing, service levels and telephony are set out in our guide to call center outsourcing in the Philippines, and the compliance layer on this page sits on top of it.
A 3.1-day case cycle is a conversion leak, not just a cost line. Origination, document review, and underwriting support resolved in-session — 97%+ of cases — with underwriters owning every final call.
Settlement doesn’t keep business hours and neither does its exception queue. Reconciliation, settlement, and chargeback operations at institutional scale under continuous telemetry.
Here the product is the audit trail. Controllership-grade reconciliations, regulatory reporting, and client servicing under SEC/FINRA/FCA disclosure discipline.
Agentic layer acts. Forensic analysts adjudicate. Telemetry never blinks.
The agentic layer absorbs the volume; forensic analysts own the judgment; continuous telemetry replaces the 270-day exposure window with a 60-second one. You own the risk policy and every regulatory decision — the architecture executes it.
Why has PCI-DSS 4.0 made the traditional Philippine KYC model legally indefensible?
Because PCI-DSS 4.0 made continuous control monitoring mandatory, not optional. Requirement 10.7 introduced continuous control monitoring with real-time alerting as mandatory — not best practice. This single shift rendered every periodic-audit KYC architecture structurally non-compliant by design, regardless of certification status.
“A passing PCI-DSS audit only tells me what a CRO’s posture looked like on one good day. It says nothing about day 91 — the silent stretch where most real exposure lives. Version 4.0 draws that line in the architecture itself: the gap has to be closed by design, not managed after the fact.”
How did synthetic-identity fraud become the primary stress test for Philippine KYC in 2026?
It grew 340% in ASEAN-originated applications between 2023 and 2026 — and binary KYC is architecturally blind to it. Composite identities pass every individual field check while failing forensic pattern analysis. Detection requires an institutional forensic library and a human analyst with jurisdictional domain knowledge — not a first-generation LLM overlay.
A legitimate Thai national ID number, a Filipino biometric selfie with a generative-AI overlay, and a real US credit history. Each element passes. The composite evaded six of seven automated platforms we tested.
vs. 14% across peers
The Tripartite Composite has since been confirmed in applications originating from Thailand, Indonesia and the Philippines itself. With a 340% ASEAN growth trajectory, this is not an edge case — it is the primary fraud vector for 2026 and beyond.
“A synthetic identity never fails on the document — it fails on the pattern. Our forensic library exists because no first-generation model has ever caught a Tripartite Composite without a human analyst who had seen one before.”
What does RAYVI reveal that cost-per-FTE conceals?
It exposes the true cost of every missed verification — fraud loss and compliance remediation that the FTE invoice hides. Risk-Adjusted Yield per Verified Identity divides total KYC cost by identities verified with no downstream fraud loss or penalty. A US digital lender restructured a 150-FTE legacy operation into a 40-specialist + AI team in Q4 2025 — and the picture inverted.
RAYVI (Risk-Adjusted Yield per Verified Identity) is a KYC performance metric that divides total operational cost by the number of identities verified with no downstream fraud loss or compliance penalty — measuring clean verifications, not headcount hours.
Yes — here is the cost-per-FTE math. Then look at what it hides.
Every procurement process starts with this table, so we publish it. But read it the way a CRO reads a passing audit: true on the day, silent about the exposure.
The FTE lens prices the seat. RAYVI prices the outcome. The savings row above is real. It is also the smaller number — −81% measured in RAYVI (cost per clean verification, inclusive of fraud loss and remediation); seat-cost savings alone run 70–78%, depending on the ratio of forensic roles to volume roles. We confirm exact figures — in both lenses — against your workflow inventory.
Indicative 2026 Manila sourcing rates — published, banded, and tied to the audit.
We publish rate bands for one reason: a quote materially below band is a Step 04 signal. Forensic talent — SEC/FINRA/FCA fluency, a live synthetic-ID pattern library, survivorship of live domain interrogation — prices inside these ranges. Below them, you are buying the 26% miss rate.
Bands reflect analysts who survive live interrogation — 81% of credentialed candidates do not. Rates confirmed per engagement against role mix and regulatory scope.
Price my role mix against the audit standard →What is the Seven-Step FinOps Vendor Audit — and which filter eliminates 81%?
Step 04 — Forensic Talent Depth — eliminates 81% of qualified-looking providers through live domain interrogation. Progressive forensic filters across a 100-vendor cohort. Credible certifications and modern stacks do not survive forensic talent depth — live domain interrogation, not credentials on paper.
PCI-DSS 4.0, SOC 2 Type II, BSP Circular 1140 and continuous audit telemetry. Vendors without a live compliance posture are removed first.
8 eliminated · 100 → 92Non-persistent VDI, biometric MFA, session isolation and PII sovereignty. The cardholder data environment must be architecturally sealed.
14 eliminated · 92 → 78HITL escalation rate, auto-resolution accuracy and decision-gate architecture. We test the orchestration, not the marketing.
27 eliminated · 78 → 51SEC/FINRA/FCA fluency, a live synthetic-ID pattern library and a live interrogation test. This is where credibility collapses — credentials do not substitute for live domain interrogation. The single largest elimination in the audit.
32 eliminated · 81% cumulative · 51 → 19RAYVI-based contracts, outcome pricing and no hourly volume incentives. Compensation must reward verified accuracy, not headcount hours.
19 retained24/7 follow-the-sun delivery, an unannounced 3AM live drill and measured BCP activation timing. Resilience is tested, never assumed.
19 retainedA real-time SLA dashboard with enforced governance. Survivors earn PITON-Global FinOps Certified status and a protected engagement structure.
19 certified ✓Why do fintechs that treat KYC as a cost center underperform?
Because cost-optimized KYC silently generates the fraud and remediation losses it appears to save. The lenders with the lowest cost-per-FTE contracts carry the highest fraud losses, the slowest origination and the largest remediation spend. Tie compensation to RAYVI and you spend less — by not absorbing the losses the cheap model silently generates.
Book a 45-Minute Call →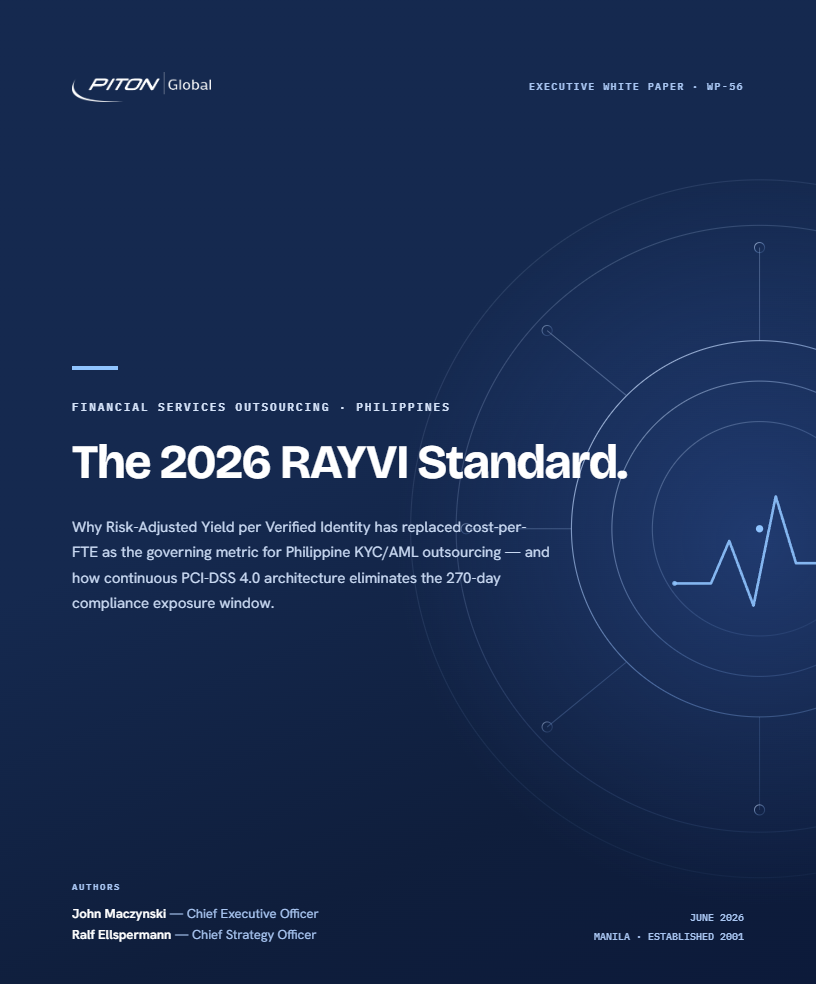
The 2026 RAYVI Standard
A 15-page institutional report on why Risk-Adjusted Yield per Verified Identity has replaced cost-per-FTE as the governing metric for Philippine KYC/AML outsourcing — and how continuous PCI-DSS 4.0 architecture eliminates the 270-day compliance exposure window legacy BPO models silently generate.
Independent coverage. Third-party validation.
What risk and operations leaders ask before outsourcing regulated workflows.
What defines institutional-grade financial-services outsourcing in 2026?+
Which financial-services functions can be outsourced?+
How is regulatory compliance actually maintained — not just certified?+
Does Agentic AI replace the human analysts?+
What does it save us?+
How fast can a team be live?+
Who owns the risk policy?+
Going deeper on financial services outsourcing
The complete index of this cluster lives in our financial services outsourcing strategy blueprint, which walks through fourteen regulated functions one by one. What follows is a buyer’s route through the rest of our writing on financial services BPO, grouped by the decision each piece helps you make.
Where the savings really come from
Start with the business case, because the cheapest seat is rarely the cheapest outcome in a regulated operation. Price the work per clean, compliant result, count rework and remediation, and ask how the model changes as volume grows. Our 2026 strategy overview for financial firms is the right first read, and the cost and efficiency trade-offs fintech operators face sets out why headcount alone misleads.
Customer care, CX and round-the-clock coverage
Customer-facing work is where a finance brand earns or loses trust, so define tone, escalation and complaint handling before you define seat counts. Decide early which channels run around the clock and which languages you need, because both change the staffing model more than volume does.
Our playbooks cover customer service, support and care for financial brands, front-office growth functions, 24/7 omnichannel support and support in more than one language. The cluster’s own customer experience blueprint ties those threads together, and for teams blending automation into the queue there is a guide to agentic voice operations.
Back office, receivables and collections
Back-office work moves fastest when the process is documented and the controls are written into the contract, not left to the vendor’s discretion. Map every hand-off to your own systems, agree the maker-checker points, and treat collections as a regulated conversation rather than a volume game.
For cash flow, compare receivables management for financial firms with a compliant approach to delinquent accounts, then go deeper with the cluster’s collections blueprint.
Fraud, risk and compliance
This is the work that decides whether a regulator ever hears your vendor’s name. Insist on continuous monitoring rather than periodic attestation, keep every risk decision on your side of the contract, and audit the data environment before the first file moves. Our planned financial compliance and risk hub will gather this work in one place.
Until then, the KYC and AML compliance blueprint and the fraud prevention blueprint are the two cluster pieces to read first.
Payments, lending and fintech
Payments and lending run on exceptions: the reconciliation break, the stalled application, the dispute that crosses a network deadline. Scope the exception queue as carefully as the happy path, and make sure coverage matches settlement windows rather than office hours. Our planned payments and wallet support hub will collect this work.
Fintech companies have their own sub-hub: the fintech outsourcing hub covers onboarding, platform support and fraud for digital-first firms, and the fintech strategy guide indexes every article in that cluster.
Technology, AI and the human layer
The practical question is not whether to use automation but where a human must stay in the loop, and who signs the decision. Ask vendors to show the hand-off between model and analyst on a real case, and to explain how that boundary is audited.
For the staffing math, read the human-to-AI ratio question; for the risk side, why anti-money-laundering work still needs human-led AI.
Building the team and holding quality
Quality in finance is a control, not a score, so agree calibration, sampling and error definitions before launch. Hire for domain literacy first; product training on complex financial technology takes longer than most buyers plan for.
What it costs
Rates for regulated finance work depend on the role mix, the compliance environment and how much of the queue automation absorbs, so any single number without that context is misleading. Our pricing page and savings calculator shows the fully loaded model we use, and a shortlist confirms final rates through a competitive RFP.
Choosing a vendor
Most vendors claim finance experience; far fewer can prove it under audit. Our seven-step vendor vetting framework is the method behind every shortlist, from scope analytics through forensic diligence to launch governance, and the case for a vendor-neutral advisory model explains why we stay independent of the providers we assess.
Finance programs rarely stand alone. If your book includes deposit or credit products, the banking hub covers bank-specific operations, and carriers and MGAs will find claims and policy work on the insurance hub.